
Track buried risks in one place
Incidents can be handled once they happen. But "concerns that could eventually lead to an incident" tend to stay scattered across Slack threads, review comments, and people's heads, left unattended without anyone taking stock of them.
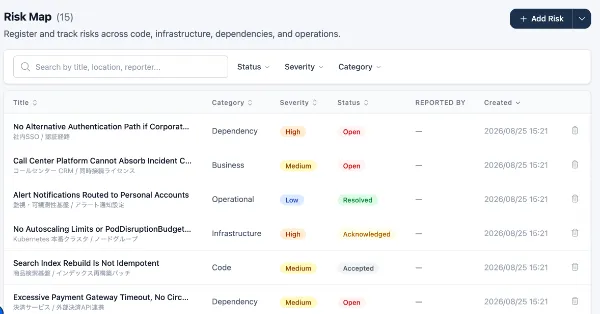
The newly released Risk Map lets you register and track these risks centrally across areas such as code, infrastructure, dependencies, business, and operations. You can access it from "Risk Map" in the sidebar.
Key features
1. Register and track risks
Risks are structured and managed along three dimensions: category, severity, and status.
- Category (5 types): Code / Infrastructure / Dependencies / Business / Operations
- Severity (5 levels): Critical / High / Medium / Low / Informational
- Status (6 types): Open / Acknowledged / In Progress / Resolved / Accepted / Duplicate
A notable feature is the "Accepted" status. You don't need to eliminate every risk; in risk management, being able to record that a risk was accepted as a deliberate decision is what matters.
The list view supports search by title, location, and reporter; filtering by status, severity, and category (multiple selections allowed); and sorting by any column.
2. Link risks to incidents and CMDB services
From the risk details screen, you can link existing incidents and services in the CMDB.
This lets you trace in both directions: "What risks remain for this service?" and "Which past incidents are the basis for this risk?" You can jump to the details page of any linked incident or service with one click.
3. AI suggests potential risks from past incidents
The biggest hurdle in risk management is identifying what the risks are in the first place.
The Risk Map includes a feature in which AI analyzes resolved incidents and suggests potential risks that have not yet been registered. Run "Identify potential risks" from the list view, and AI analyzes recent resolved incidents (up to 100) holistically and presents 3 to 10 candidate risks.
Each candidate includes a title, category, and severity, along with the rationale for why it was judged to be a risk and the names of the actual incidents behind it. Review the results and register only the ones you need in bulk. Output is available in both Japanese and English.
It is especially effective at uncovering patterns such as "the same type of failure keeps recurring, but the root cause has never been addressed."
4. Automatic risk creation from CVE scans
If you add tags in the format tech:<product-name> to services in the CMDB, they are automatically matched against vulnerability (CVE) scan results, and matching vulnerabilities are automatically registered as risks in the Dependencies category.
- Severity is determined automatically from the CVSS score (9.0 or higher: Critical; 7.0 or higher: High; 4.0 or higher: Medium; 0.1 or higher: Low)
- Risks for the same product are consolidated into a single entry, and each newly found CVE is added to its list of related CVEs
- Severity is raised only when a more serious CVE is detected later. Titles and descriptions your team has edited are never overwritten
- Related CVEs are displayed with links to the NVD
Vulnerabilities in dependency packages are continuously added to your risk register without manual effort.
5. Change history
All changes to fields, including severity and status, as well as incident and service linking operations, are recorded in the audit log. In the "Change history" section of the risk details screen, you can see a timeline of who changed what and when.
Because you can later trace "when was this risk accepted?", the history can also serve as evidence for audits.
6. Public API support
The Risk Map is also available through the Public API, so you can automatically create risks from external tools such as CI/CD pipelines and security scanners.
- List:
GET /v1/risks - Create:
POST /v1/risks - Get:
GET /v1/risks/{id} - Update:
PATCH /v1/risks/{id} - Link incident:
POST /v1/risks/{id}/link-incident
Permissions
Admins and members can create, edit, delete, and link risks. Users with the Viewer role see a read-only screen, and editing actions are not displayed.
Getting started
- Open "Risk Map" in the sidebar
- We recommend starting with "Identify potential risks" to surface candidate risks from past incidents
- Link the related CMDB services and incidents to the risks you've identified
- To automatically pick up vulnerabilities in dependencies, add
tech:<product-name>tags to your CMDB services